
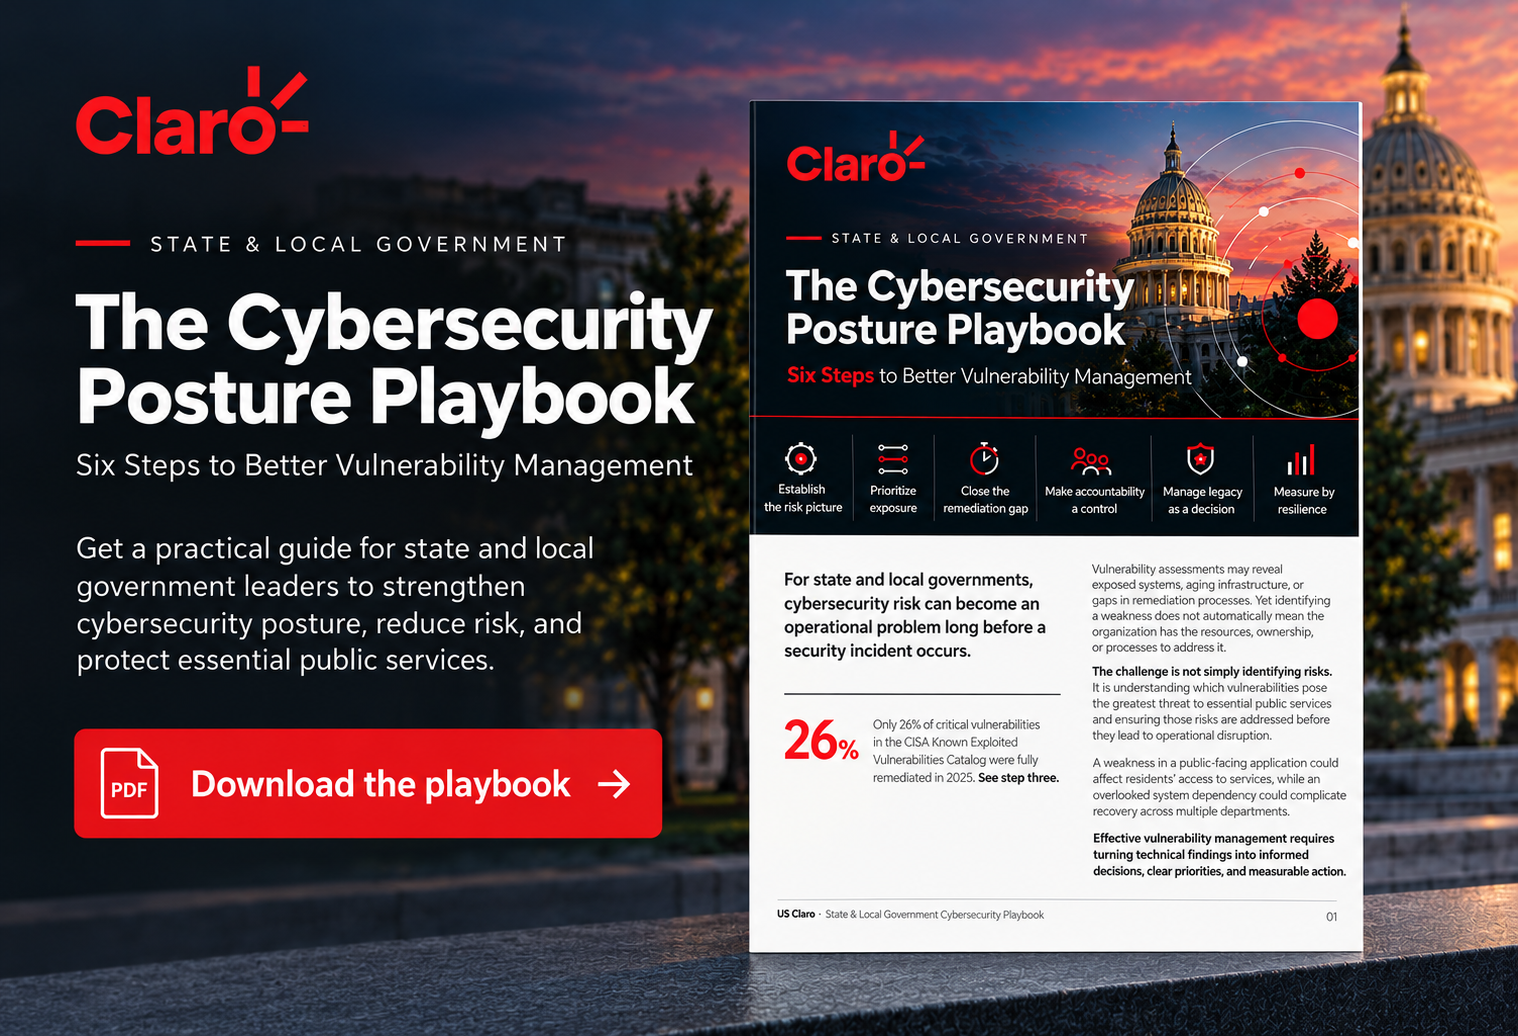
Six steps to better vulnerability management

For state and local governments, cybersecurity risk can become an operational problem long before a security incident occurs.
Vulnerability assessments may reveal exposed systems, aging infrastructure, or gaps in remediation processes. Yet identifying a weakness does not automatically mean the organization has the resources, ownership, or processes to address it.
The challenge is not simply identifying risks. It is understanding which vulnerabilities pose the greatest threat to essential public services and ensuring those risks are addressed before they lead to operational disruption.
A weakness in a public-facing application could affect residents' access to services, while an overlooked system dependency could complicate recovery across multiple departments.
Effective vulnerability management requires turning technical findings into informed decisions, clear priorities, and measurable action.
Six steps to stronger cybersecurity posture
For state and local government executives, the following six recommendations provide a practical framework for strengthening cybersecurity posture, reducing operational exposure, and building long-term resilience.
These steps help leadership move beyond vulnerability reporting toward informed decisions and measurable risk reduction.
1. Establish the risk picture
A vulnerability scan tells you where weaknesses exist, but cybersecurity posture tells you what those weaknesses mean. That distinction should shape how leaders evaluate risk.
Consider two vulnerabilities with the same technical severity. One affects an isolated internal application. The other sits within an internet-facing system supporting an essential public service.
The severity score may be identical.
The consequence is not.
Effective vulnerability management therefore begins with context. Leadership needs a current understanding of:
- Critical systems and the services they support
- Internet-facing assets and applications
- Hardware, software, cloud, and connected assets
- Unsupported and legacy technology
- Known vulnerabilities and active exploitation
- Third-party dependencies
- Security controls and monitoring coverage
- Ownership of critical assets and remediation
CISA recommends maintaining a regularly updated inventory of organizational assets because asset visibility supports vulnerability detection and remediation.
For executives, the objective is not perfect technical inventory. It is decision-quality visibility.
Leadership should be able to see where technology exposure intersects with operational consequence.
2. Prioritize exposure, not vulnerability counts
Large vulnerability reports can create the appearance of precision without providing much direction.
A government organization may have thousands of open findings. That number alone says very little about its actual level of risk.
The more consequential questions are:
Which vulnerabilities are most likely to be exploited, and what happens if they are?
Prioritization should account for:
- Evidence of active exploitation
- Internet exposure
- Criticality of the affected service
- Access to sensitive or citizen data
- Availability of compensating controls
- Dependencies on other systems
- Potential operational impact
A mature program does not ask teams to address everything at once. It creates a defensible order of operations.
3. Close the distance between identification and remediation
A persistent challenge for public-sector organizations is that knowing about risk does not mean the organization is reducing it.
That gap deserves executive attention.
According to Verizon's 2026 public-sector analysis, only 26% of critical vulnerabilities in the CISA Known Exploited Vulnerabilities Catalog were fully remediated by organizations in 2025. Median time to full resolution reached 43 days.
That makes remediation performance as important as detection capability.
Executives should look beyond how many vulnerabilities security teams discover and instead ask whether exposure is actually declining.

The objective is not to drive every number to zero.
It is to demonstrate that the organization's most consequential risks are being reduced at an acceptable pace.
4. Make accountability part of the control environment
Technology can identify a vulnerability. It cannot resolve unclear ownership.
Remediation often crosses organizational boundaries. Security may identify the exposure. IT may own the infrastructure. An agency may own the application. A vendor may manage the platform. Another department may need to approve downtime.
Without clear accountability, a critical vulnerability can remain open while everyone assumes someone else is addressing it.
Leadership should establish:
- Who owns the affected asset
- Who owns remediation
- Who can accept or defer risk
- When unresolved risk must be escalated
- What requires executive visibility
This is where governance becomes a security control in its own right.
A vulnerability without an accountable owner is an unmanaged risk.
5. Manage legacy technology as a risk decision
State and local governments cannot modernize every system simultaneously.
Legacy platforms may support essential services long after vendors stop providing security updates. Replacing them can require significant funding, procurement, integration, and operational planning.
That reality does not eliminate the risk.
It changes how the risk must be managed.
For critical legacy technology, leadership should make an explicit decision:
Modernize it. Isolate it. Apply compensating controls. Or formally accept the risk.
CISA recommends isolating legacy systems, monitoring them for unusual activity, and developing migration plans toward supported platforms.
What should not become an operating model is allowing known exposure to persist indefinitely because remediation is difficult.
6. Measure posture by resilience, not prevention alone
Even strong vulnerability management cannot guarantee that every weakness will be identified and remediated before an attacker finds it.
That is why cybersecurity posture ultimately extends beyond prevention.
NIST Cybersecurity Framework 2.0 organizes cybersecurity risk management around six functions:
Govern. Identify. Protect. Detect. Respond. Recover.
Together, they establish a broader standard for executive oversight.
The organization must reduce preventable exposure while maintaining the ability to contain incidents and restore critical services when prevention fails.
For government, resilience has a practical definition:
Can essential services continue—or be restored quickly—when technology is disrupted?
That is ultimately the standard against which cybersecurity posture should be judged.
The executive test
A mature vulnerability management program should give leadership clear answers to a relatively small set of consequential questions:
- What are our most significant cyber exposures today?
- Which critical government services depend on those systems?
- Are any known vulnerabilities being actively exploited?
- Who is accountable for remediation?
- How quickly are our highest-risk exposures being reduced?
- Where are legacy systems creating risk we cannot readily eliminate?
- Can essential services continue or recover if those controls fail?
The value of cybersecurity posture is not a longer vulnerability report. It is the ability to make better risk decisions. Across state and local government, the executive imperative is to keep technical visibility and operational action connected—with enough context to prioritize risk, enough accountability to drive remediation, and enough resilience to protect the public services that depend on both.
Download the playbook for six practical steps to strengthen cybersecurity posture, reduce vulnerabilities, and protect essential public services.
FAQ
How can state and local governments strengthen their cybersecurity posture?
State and local governments can strengthen cybersecurity posture by improving asset visibility, prioritizing critical vulnerabilities, establishing remediation accountability, managing legacy technology, and building resilience to protect essential public services.
Why should government agencies prioritize cybersecurity exposure over vulnerability counts?
Vulnerability counts alone do not reflect operational risk. Government agencies should prioritize weaknesses based on active exploitation, internet exposure, service criticality, system dependencies, and potential disruption to essential services.
How can government leaders improve vulnerability remediation?
Government leaders can improve remediation by assigning clear ownership, establishing escalation procedures, tracking resolution times, and measuring whether high-risk exposures are declining rather than simply counting identified vulnerabilities.
How should state and local governments manage cybersecurity risks associated with legacy systems?
Government agencies should evaluate legacy systems based on operational importance and exposure, then determine whether to modernize, isolate, implement compensating controls, or formally accept the associated cybersecurity risks.
Insights
Stay up to date on pivotal trends in information technology that are set to define the future of business. Subscribe to our blog today!



Our Core Capabilities

INFRASTRUCTURE
& CONNECTIVITY
connectivity and cloud.


SECURITY

DIGITAL INNOVATION
& HYPER-AUTOMATION

INTELLIGENT
INSIGHTS & AI

TALENT
EXTENSION
