

Measuring security awareness: Metrics that matter
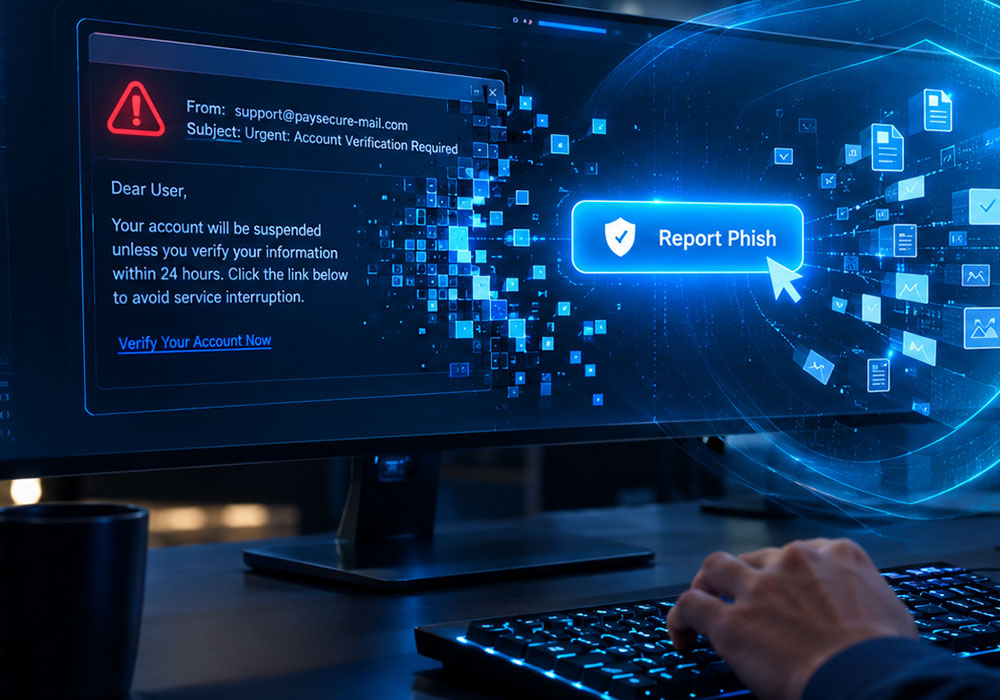

Most organizations can answer a basic question about security awareness training: Who completed it?
That matters for compliance. But it does not answer the question security, and business leaders ultimately need answered:
Is workforce-related cyber risk actually decreasing?
Training completion measures participation—not behavior. A stronger measurement strategy looks at how employees recognize, report and respond to threats, where risky behaviors persist and whether the organization's overall human risk profile is improving.
Effective security awareness measurement goes beyond completion rates to track behavioral risk, threat reporting, repeat behaviors, response patterns and organizational exposure over time.
Completion is a starting point
Completion rates provide an important baseline. They demonstrate participation and can support regulatory, audit and policy requirements.
But an employee completing a training module does not necessarily mean that employee will recognize a sophisticated phishing attempt three months later.
NIST has specifically identified the need for security awareness programs to move beyond compliance-focused measures toward evidence of changes in employee attitudes and behaviors.
For IT and security leaders, that means the measurement question should evolve from "Did employees take the training?" to "Are employees becoming less likely to introduce risk?"
Measure behavior, not just participation
No single metric provides that answer.
Even phishing click rates can be misleading when viewed alone. The difficulty of simulated phishing messages varies, and NIST cautions that click and reporting rates provide only part of the picture.
A more useful view combines several indicators.
Reporting behavior
Employees who recognize and quickly report suspicious activity can become an important part of early threat detection.
Track:
- Phishing reporting rates.
- Time between receipt and reporting.
- Reporting trends over time.
- Differences across departments or user groups.
An increase in legitimate reporting can be a positive signal, even if the raw number of reported incidents rises.
Repeat behavior
Organization-wide averages can hide concentrated risk.
If overall phishing performance improves but the same employees repeatedly click simulated malicious links, the organization still has a measurable area of exposure.
Tracking repeat behaviors helps identify where additional education or more targeted intervention may be required.
Behavioral risk
Different employees create different levels of potential exposure based on their behavior, role, access and susceptibility to threats.
Rather than treating every employee identically, organizations can use behavioral signals and risk scoring to identify higher-risk users and adapt training accordingly.
This shifts security awareness from a standardized exercise toward a more risk-based program.
Security incidents
Training data becomes more meaningful when considered alongside actual security outcomes.
Organizations can examine trends in incidents associated with behaviors such as credential sharing, phishing, improper data handling or other preventable actions.
The objective is not necessarily to drive every incident metric to zero. Greater awareness may initially increase reporting because employees are more likely to recognize and escalate suspicious activity.
Organizational exposure
Ultimately, leaders need to understand what workforce behavior means for the business.
That requires looking across individual training metrics to identify:
- Which groups demonstrate greater susceptibility?
- Where do risky behaviors repeatedly occur?
- Are reporting behaviors improving?
- Are high-risk users improving after targeted intervention?
- Is human-related exposure trending in the right direction?
This turns awareness data into information leaders can use to prioritize risk.
Use measurement to change the program
Measurement has limited value if every employee continues receiving the same training regardless of the results.
A mature program creates a feedback loop:
Measure behavior - identify risk - adjust training - test again - measure improvement
This is where newer security awareness capabilities can make a difference.
Claro's Managed Security Awareness Training, for example, combines phishing simulations, behavioral analysis, AI-based risk scoring and adaptive training. Training frequency and content can change based on individual risk signals rather than relying exclusively on a fixed training schedule.
The important capability is not AI itself. It is the ability to use measurement to make training more relevant to the risks actually appearing within the workforce.
Give leaders a clearer view of human risk
Security awareness should still satisfy compliance requirements. Completion rates should still be tracked.
They simply should not be mistaken for proof that the program is working.
For decision-makers, the more valuable question is whether employees are demonstrating safer behaviors and whether areas of elevated risk are being identified and addressed.
That requires moving beyond:
How many people completed security training?
toward:
What does workforce behavior tell us about our exposure, and is that exposure improving?
When security awareness programs can answer that question, training becomes more than an annual requirement. It becomes a measurable component of cyber risk management.
FAQs
How should organizations measure security awareness training effectiveness?
Organizations should combine completion data with behavioral measures such as phishing reporting, response time, repeat risky behaviors, risk trends and relevant security incidents.
Are phishing click rates enough to measure security awareness?
No. Click rates provide useful information but should be evaluated alongside reporting behavior, phishing difficulty, repeat behaviors and other indicators of workforce-related risk.
What is human risk in cybersecurity?
Human risk is the potential security exposure associated with employee behaviors, access and interactions with threats, including phishing, social engineering, credential misuse and improper handling of information.
How can security awareness training reduce human risk?
Effective programs identify risky behaviors, deliver relevant education, reinforce secure practices and continually measure whether employees become better at recognizing, reporting and responding to threats.
What is adaptive security awareness training?
Adaptive training adjusts content, frequency or interventions based on employee behavior and risk signals, allowing organizations to focus additional education on users or groups demonstrating greater exposure.
Insights
Stay up to date on pivotal trends in information technology that are set to define the future of business. Subscribe to our blog today!



Our Core Capabilities

INFRASTRUCTURE
& CONNECTIVITY
connectivity and cloud.


SECURITY

DIGITAL INNOVATION
& HYPER-AUTOMATION

INTELLIGENT
INSIGHTS & AI

TALENT
EXTENSION
